wordpress
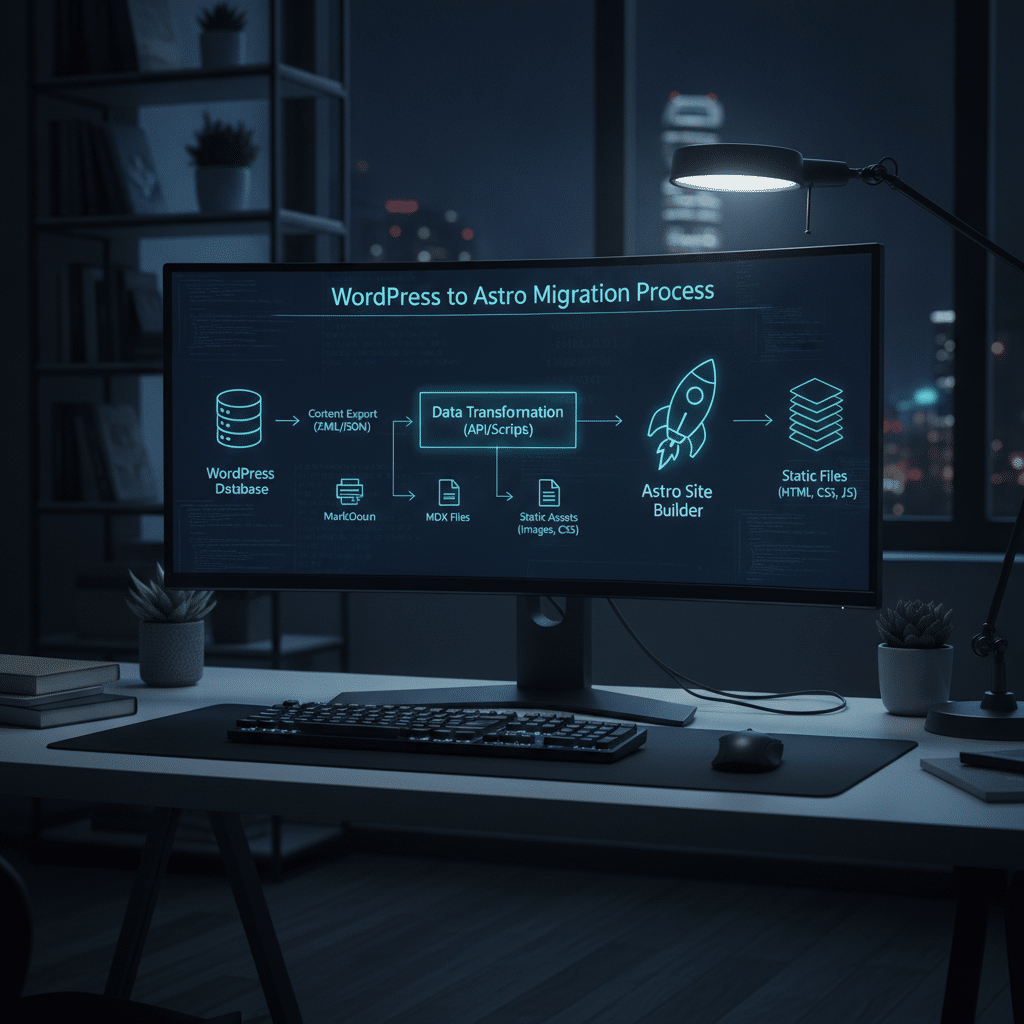
WordPress to Astro Migration: Complete Guide and Lessons
A comprehensive guide to migrating from WordPress to Astro static site generator, covering content conversion, performance optimization, and SEO preservation with practical implementation strategies.
Read More
WordPress 7.1.3 Security Update Patches Critical Vulnerabilities
WordPress 7.1.3 patches critical security flaws including XSS, SQL injection, and information disclosure vulnerabilities. Site owners must update immediately to protect against active threats.
Read More
Automattic Wants WordPress Despite Not Owning It
Automattic maintains significant influence over WordPress despite not owning the open-source platform. The relationship between the commercial company and the WordPress Foundation creates complex dynamics within the ecosystem.
Read More
WordPress Patches Critical Code Execution Flaw CVE-2026-87902
WordPress released version 7.1.2 to patch CVE-2026-87902, a critical vulnerability affecting versions 4.7.0 through 7.1.1. The flaw allows unauthenticated attackers to load PHP files outside theme folders, potentially enabling code execution on certain server configurations.
Read More
Disguising WordPress Sites: Security Through Obscurity Explained
WordPress powers 43% of websites, making it a prime target for automated attacks. While hiding WordPress fingerprints won’t stop determined hackers, it can reduce automated scanning and improve your overall security posture.
Read MoreWordPress 7.1.2 Security Update Patches Critical Vulnerability
WordPress 7.1.2 patches a critical template resolution vulnerability that allows unauthenticated attacks. Plus: Ipsum becomes the new default theme, ending 16 years of calendar-based naming.
Read More
Critical WordPress Flaw Under Active Exploitation by Hackers
Hackers actively exploit a critical WordPress vulnerability enabling remote code execution. Website owners must update immediately to protect against CVE-2025-4225 attacks targeting millions of sites.
Read More
New WordPress CSRF Vulnerability Exploit Details Released
Security researchers have released technical details and a working exploit for a new cross-site request forgery vulnerability affecting WordPress sites. The disclosure raises immediate concerns about site security and necessary protective measures.
Read More
WordPress 7.1.2 Security Update Patches Critical RCE Vulnerability
WordPress 7.1.2 addresses a critical remote code execution vulnerability that could allow unauthenticated attackers to compromise vulnerable websites. Site administrators should update immediately to protect their installations.
Read More
Critical WordPress Vulnerability CVE-2026-87902 Under Active Exploit
Critical WordPress vulnerability CVE-2026-87902 enables remote code execution and is under active exploitation. All versions from 4.7.0 to 7.1.1 are affected. Organizations must update immediately to version 7.1.2 or newer to protect against ongoing attacks.
Read More